CISA adds exploited Palo Alto Networks PAN-OS management flaw to KEV catalog
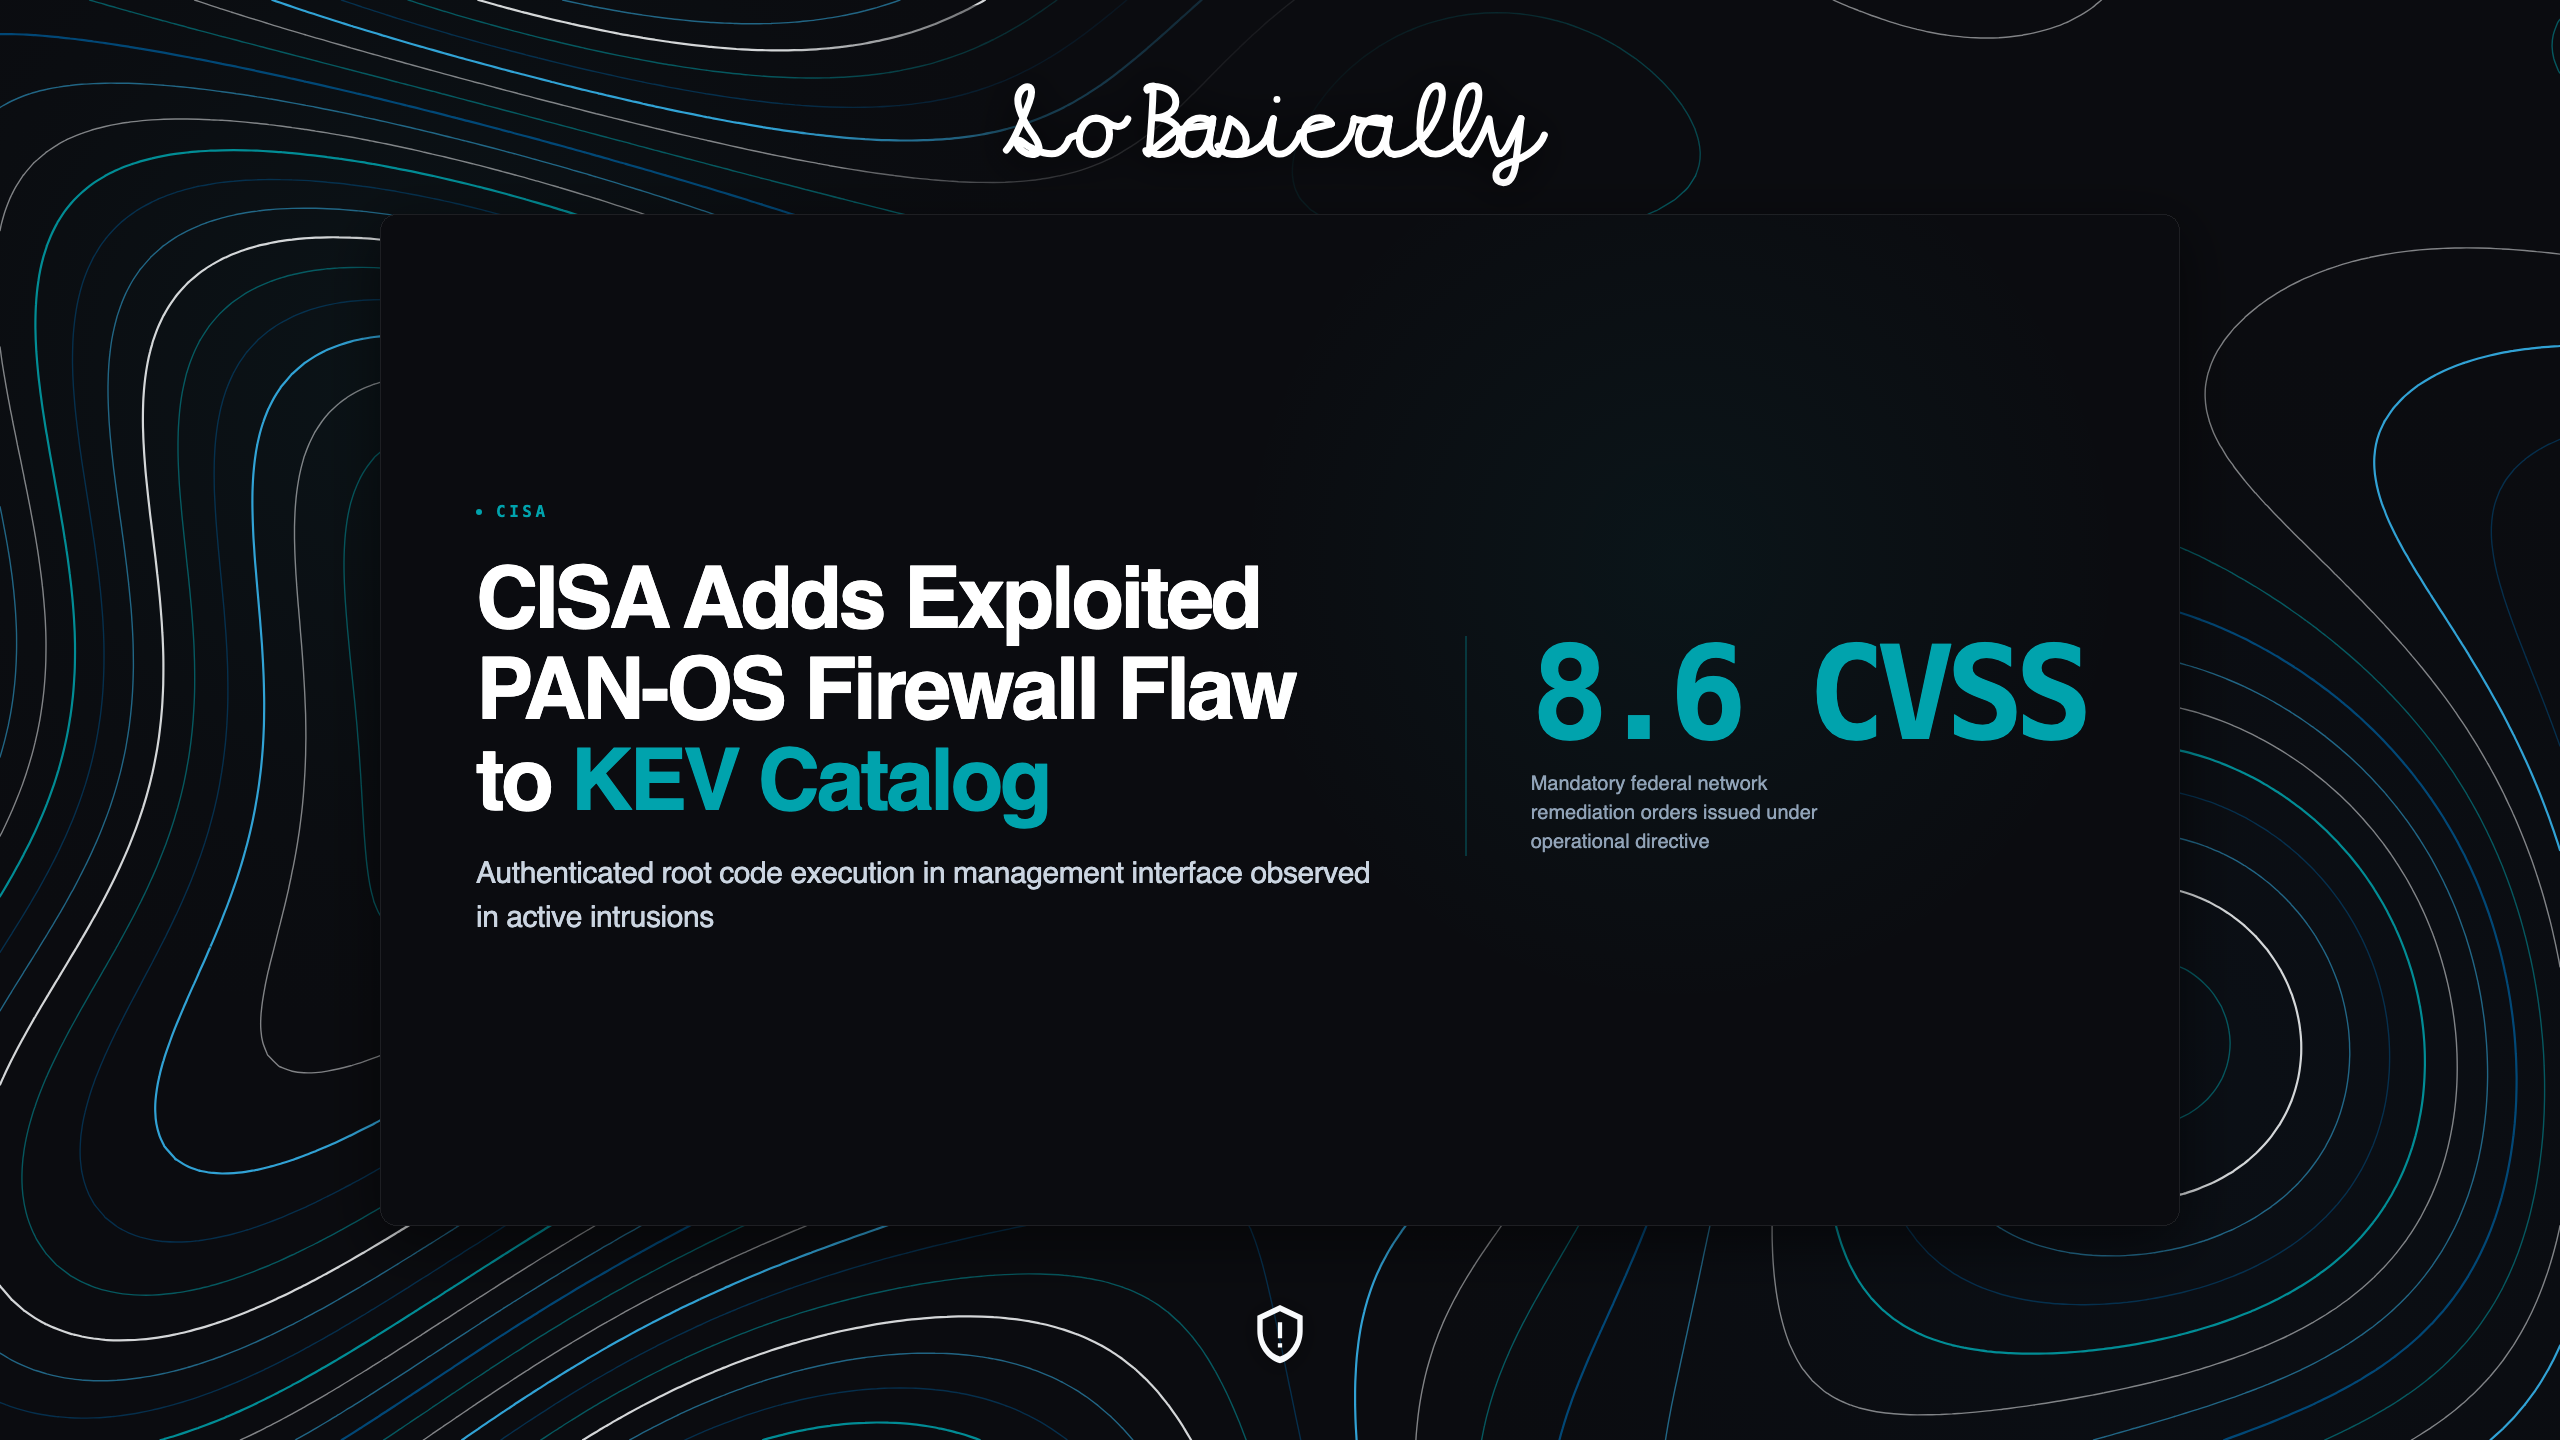
What happened.CISA added an actively exploited remote code execution vulnerability in the Palo Alto Networks PAN-OS management interface to its Known Exploited Vulnerabilities catalog.
Why it matters.Enterprise edge firewalls protect perimeter boundaries, and root-level command access allows threat actors to disable intrusion telemetry and pivot silently into internal subnets. Security teams should restrict all PAN-OS administrative interfaces to internal management networks and apply available vendor patches immediately.